Blog
Inside the Conscia SOC: Why modern MDR is a business enabler, not just a safety net
Cybersecurity is not about drama. It is about discipline, engineering and trust. Inside Conscia’s Security Operations Centre (SOC), that principle shapes everything we do. Traditional security technology can make the doors smaller, but determined attackers may still find a way in. Managed Detection and Response (MDR) is one of the most effective ways to reduce […]
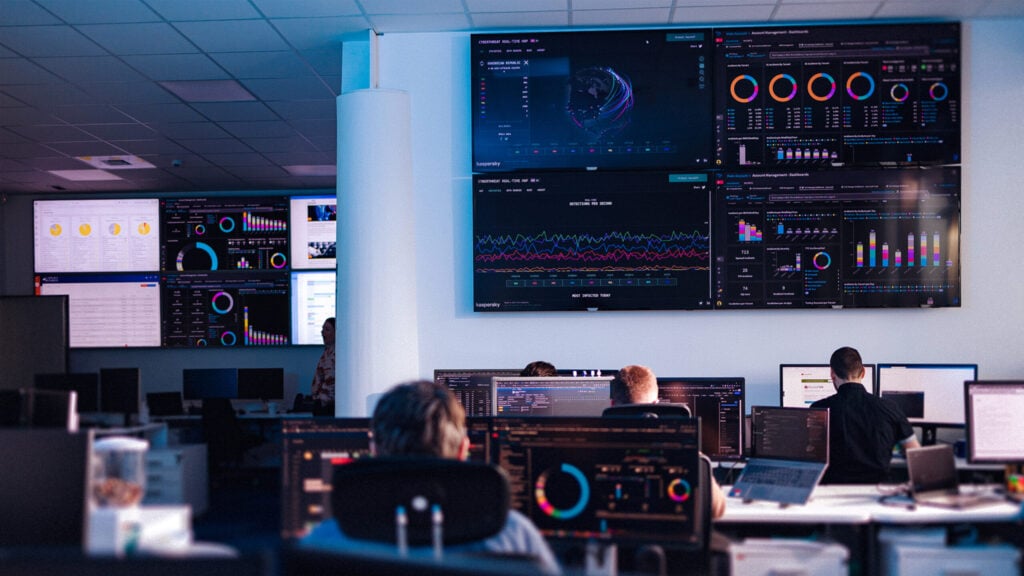
Cybersecurity is not about drama. It is about discipline, engineering and trust. Inside Conscia’s Security Operations Centre (SOC), that principle shapes everything we do.
Traditional security technology can make the doors smaller, but determined attackers may still find a way in. Managed Detection and Response (MDR) is one of the most effective ways to reduce cyber risk to a genuinely acceptable level. We prefer to think of it not as a cost, but as a business enabler. It allows our customers to take on additional risk through innovation while helping us manage that risk on their behalf.
How managed detection and response works in a modern SOC
Modern MDR rests on two core elements working in concert: threat intelligence, which gives us the context to anticipate what is coming, and operations, the reactive engine that detects and rapidly neutralises threats.
Matic Jerman, MDR Operations Manager at Conscia, describes the operations floor as similar to a hospital emergency department. In every shift, analysts must be ready to encounter something they have never seen before, staying vigilant not only to the alert they are investigating but also to everything happening around it. That is where real threats are identified.
Speed is everything. Rather than waiting for an analyst to pick up a case, our in-house Security Orchestration, Automation and Response (SOAR) playbooks enrich alerts and take response actions automatically, increasingly before a human even opens the case. When persistence can be established in a matter of minutes, that head start matters.
Where possible, automation goes beyond containment to eradication by resetting credentials, removing rogue MFA methods and stripping persistence from the environment.
Why security operations centre analysts still matter in an automated SOC
Automation is best at what humans are worst at: volume, repetition and consistency at three in the morning. Humans are best at what automation cannot do: judgement in novel situations, understanding business context, and knowing when not to follow the playbook. These are not separate lanes. Humans build the automation, every incident teaches us what to automate next, and good automation makes analysts more expert, not less – because it frees them from the toil that would otherwise burn them out.
The right mental model is not “automation replaces analysts”, but “automation is how analysts scale themselves
Why MDR services are a partnership, not just a service desk
What sets Conscia apart is the closeness of the relationship. Our technical account managers are in regular contact with customers at a technical level, not only through management and sales channels. We meet regularly to review emerging threats and ensure that each customer’s security posture remains aligned with the evolving threat landscape.
We work alongside our customers every day, not only when incidents occur. As a result, when challenging situations arise, we can respond more effectively together.
Finally, our approach is built on defensive fusion. Rather than treating MDR, offensive security, threat intelligence, exposure management and GRC as separate disciplines, we combine them into a single capability that delivers significantly more value than the sum of its parts.
That is how cybersecurity works at Conscia. And that is the value we deliver, every single day.
Watch the video to step inside our SOC and hear how the team turns process, automation and expertise into protection you can rely on.
About the author
Peter Jones
Cyber Security Specialist, CISSP, CISM, CCSP
Peter Jones is a Cyber Security Specialist at Conscia UK. He has been in the IT industry for over 30 years, providing consulting and advisory services to both Commercial and Public Sector Accounts throughout Europe. Having previously worked for both Cisco and Microsoft, Peter combines professional and academic achievements with real world experience to support our UK business. He currently holds CISSP, CISM and CCSP certifications.
Related