Whitepaper
Early sign-up: Understand what European cyber evidence means for resilience
Be first in line for Conscia’s Cyber Resilience Insights 2026 report when it launches this October. Built on evidence from European SOC, Managed Detection & Response, forensic and offensive security work, the report helps leaders understand the conditions shaping real cyber outcomes – and the decisions that can strengthen resilience in 2027.
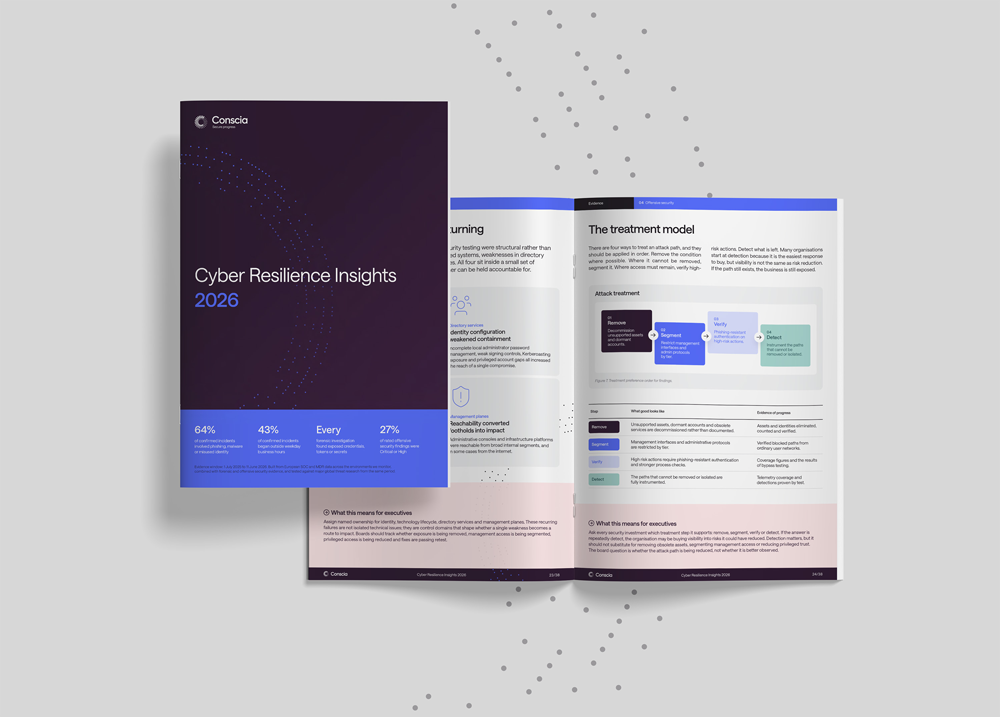
Cybersecurity leaders are under pressure to respond faster, prioritise smarter and prove that security investments reduce real-world risk. But many organisations still assess cyber risk through disconnected views of threats, tools and incidents.
That is why Conscia has created Cyber Resilience Insights 2026 – a new evidence-based report for business and technology leaders responsible for resilience, risk and continuity. The report looks beyond threat headlines to explain what our findings mean for executive decision-making, cyber investment and operational readiness.
Built on evidence from the European environments we monitor, investigate and test, the report combines data from Conscia’s Security Operations Centres, Managed Detection & Response services, forensic investigations and offensive security work. It does not only ask what happened. It asks what those findings reveal about the conditions that allowed incidents to escalate – and what leaders can do about them.
Inside the report, you will gain:
The report explains why resilience is not only about responding to the newest threat. Across monitoring, investigation and testing, familiar weaknesses appeared repeatedly: compromised identities, excessive trust, incomplete visibility and delays between detection and action.
- A clear understanding of the central findings from Cyber Resilience Insights 2026 and why they matter for business resilience.
- Evidence on how identity, trusted access, visibility gaps and response authority shaped many cyber outcomes.
- Practical guidance on how boards, CIOs, CISOs and executive teams can turn operational security evidence into better decisions.
- A structured view of six board-level decisions that should shape cyber investment and resilience planning for 2027.
- Insight into emerging risks around AI, machine identities, software supply chains and trusted automation.
Those findings matter because they are actionable. Organisations do not need to predict every threat that will emerge in 2027. They need to strengthen the foundations that determine how effectively they can prevent attacks, contain incidents and recover with confidence.
Whether you are planning cybersecurity investment, assessing resilience maturity or looking for a clearer way to discuss cyber risk with leadership, Cyber Resilience Insights 2026 will help you move from evidence to action.
Related