Whitepaper
Report: Cyber Resilience Insights 2026
Move beyond headline threat trends. Cyber Resilience Insights 2026 connects our own European SOC and MDR data, forensic investigation, offensive security testing and global threat research to show which conditions most often shape cyber outcomes.
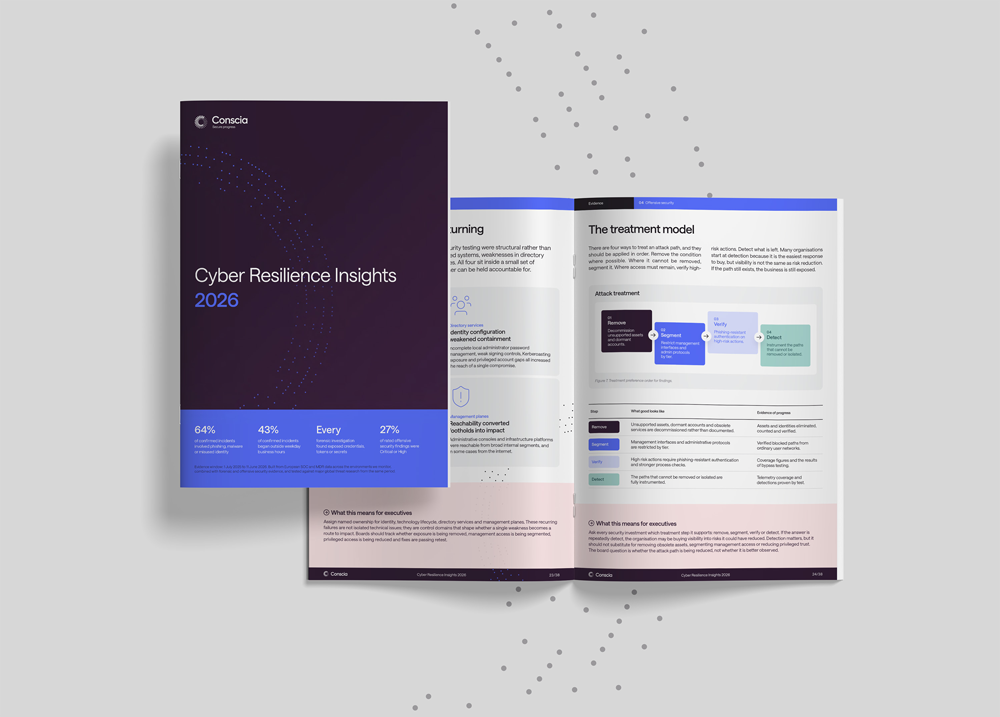
What European operational evidence reveals about cyber resilience
Cybersecurity teams are under pressure to respond faster, prioritise smarter and prove that investments reduce real-world risk. But many organisations still assess cyber risk through disconnected views of threats, tools and incidents.
This report brings those views together. Built from European environments monitored, investigated and tested by Conscia, it shows where defences held, where they failed and which decisions matter most for 2027.
The findings point to a clear conclusion: outcomes were shaped less by attacker novelty than by recurring operational conditions – compromised identities, excessive trust, incomplete visibility and delays between detection and action.
What you will learn
- Why identity remains the common denominator across incidents, investigations and testing
- How trusted systems and workflows become attack paths
- Why forensic readiness is now a board-level resilience issue
- What European SOC and MDR data reveals about detection, timing and response
- Which six board decisions should shape cyber investment in 2027
- How to measure progress through reduced exposure and improved response
Who should read it?
This report is for executives, board members, security leaders and technical decision-makers who need a practical, evidence-based view of cyber risk and a clearer way to turn that insight into action.
About the author
David Kasabji
Head of Threat Intelligence, Conscia Cyber & AI Security
David Kasabji is the Head of Threat Intelligence at the Conscia Group. He leads the development and delivery of actionable intelligence across cyber defense and managed security operations, translating complex threat activity into clear outcomes for different audiences — from SOC analysts and incident responders to executive stakeholders and external communications. His work spans end-to-end intelligence operations: collection and analysis of adversary activity, threat actor and campaign profiling, IOC and TTP development, and intelligence-driven guidance for detection, threat hunting, and security prioritization. David is also actively involved in Digital Forensics and Incident Response, supporting investigations and crisis situations with rapid triage, context, and strategic recommendations. A strong focus of his role is continuously improving how intelligence is operationalized through standardization and automation to ensure it is timely, relevant, and measurable.nd strategic crisis management during incidents.
Related