Event
What Europe’s cyber incidents reveal about the risks ahead
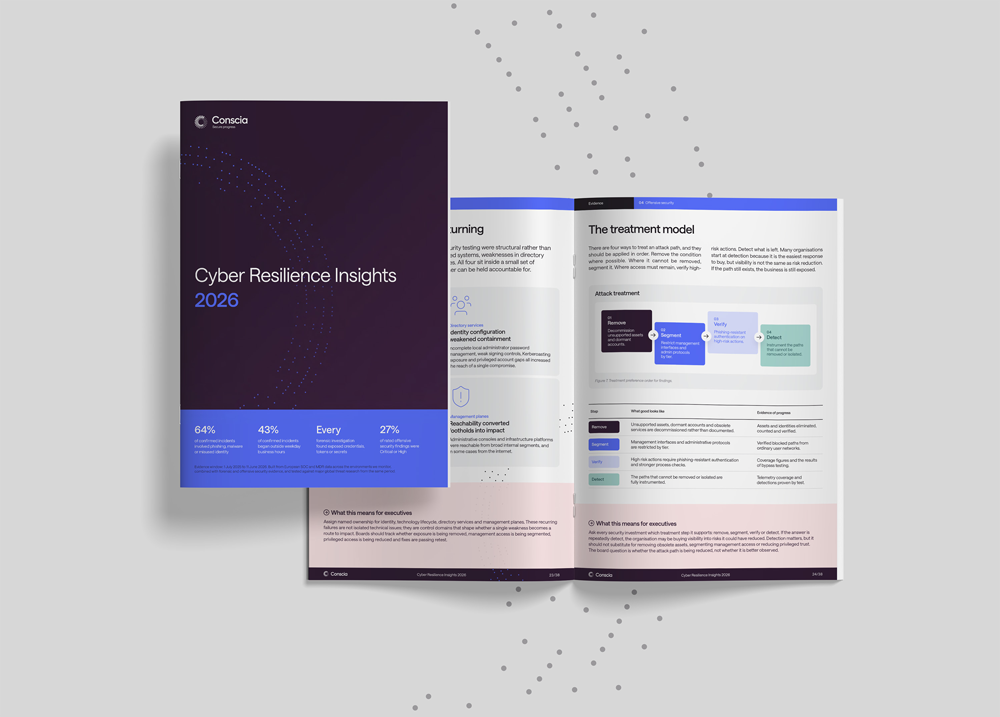
Join this webinar on Conscia’s Cyber Resilience Insights 2026 report and find out what a year of incidents across Europe shows about AI, identity, and the risks organisations underestimate.
David Kasabji
Head of Threat Intelligence, Conscia Cybersecurity
Jesper Kastoft Bertelsen
Director of Cyber Defense Services, Conscia Cybersecurity
Andrew Michal
Senior Cybersecurity Engineer, Conscia Cybersecurity
Date & time
October 29, 2026 - 10:00 - 11:00 (CET)
Where
Online
Language
English
Target audience
This webinar is designed for:
-
- CISOs and security leaders
-
- CIOs and IT decision-makers
-
- Risk and compliance professionals
-
- Executive leadership teams
-
- Board members responsible for cyber resilience and governance
Whether you are setting cyber strategy, managing security operations or overseeing organisational risk, this session will help you connect operational evidence to the decisions that shape cyber resilience, investment priorities and risk governance.
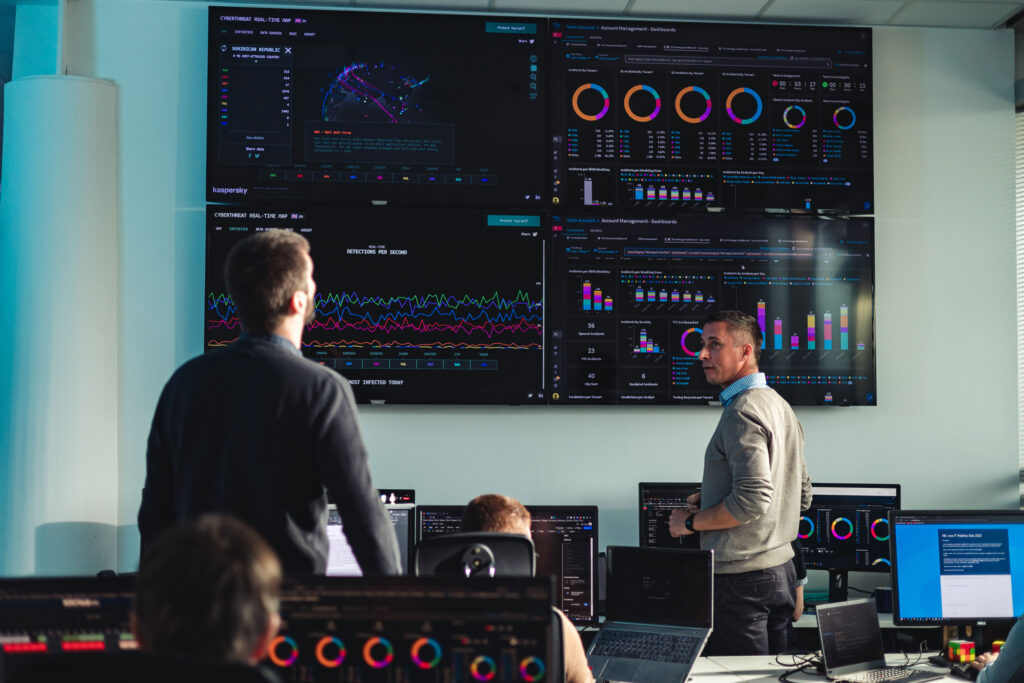
Most cyber intrusions today are still driven by the techniques we all know: Compromised identities, social engineering, vulnerability exploitation, and more. Delays between detection and reaction continue to create opportunities for attackers. AI is impacting cybersecurity, but not in the way most might think, forcing us to rethink how we assess risk, build resilience and make decisions. While new technologies dominate the headlines, many organisations are still struggling with the fundamentals.
So where should security leaders focus next?
In this webinar, our speakers David Kasabji, Jesper Kastoft Bertelsen and Andrew Michal connect the findings of Conscia’s Cyber Resilience Insights 2026 report to the real-world risks and priorities organisations need to address as they prepare for 2027
The evidence behind the discussion
- 64% of confirmed incidents involved phishing, malware or misused identity.
- 43% of confirmed incidents began outside weekday business hours.
- Every forensic investigation found exposed credentials, tokens or secrets.
- 27% of rated offensive security findings were classified as Critical or High.
Conscia’s Cyber Resilience Insights 2026 report.
Why this webinar matters
For security leaders, the challenge is about more than just understanding that cyber risk is evolving. It now revolves around deciding which risks deserve attention, which investments will strengthen resilience, and how to act with confidence in a landscape shaped by emerging technologies, shifting attacker behaviour and competing narratives.
This webinar focuses on evidence, not speculation.
It draws on real-world observations from monitoring, incident response, threat intelligence and offensive security testing to examine the risks organisations continue to underestimate, how AI is impacting the threat landscape, and which priorities security leaders should bring into strategic planning for 2027.
What we will discuss
- How AI is amplifying attacker capabilities and impacting defensive operations
- Why identity remains one of the most common pathways to compromise
- The patterns emerging across incident response, MDR and offensive security engagements
- Which cyber risks organisations are consistently underestimating
- How security leaders can distinguish genuine risks from industry hype
- What the evidence suggests organisations should prioritise as they prepare for 2027
Reserve your place today and discover which risks deserve your attention now, before they become tomorrow’s incidents.
About the speakers
David Kasabji
Head of Threat Intelligence, Conscia Cybersecurity
David Kasabji is the Head of Threat Intelligence at the Conscia Group. He leads the development and delivery of actionable intelligence across cyber defense and managed security operations, translating complex threat activity into clear outcomes for different audiences — from SOC analysts and incident responders to executive stakeholders and external communications. His work spans end-to-end intelligence operations: collection and analysis of adversary activity, threat actor and campaign profiling, IOC and TTP development, and intelligence-driven guidance for detection, threat hunting, and security prioritization. David is also actively involved in Digital Forensics and Incident Response, supporting investigations and crisis situations with rapid triage, context, and strategic recommendations. A strong focus of his role is continuously improving how intelligence is operationalized through standardization and automation to ensure it is timely, relevant, and measurable.nd strategic crisis management during incidents.
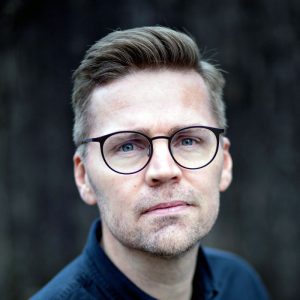
Jesper Kastoft Bertelsen
Director of Cyber Defense Services, Conscia Cybersecurity
Jesper Kastoft Bertelsen is Director of Cyber Defense Services at Conscia Cybersecurity, where he leads an organisation delivering a 24/7 detection and response service to customers. He heads a department spanning detection engineering, threat operations, frontline operations and service transition, and connects day-to-day security operations with executive leadership, turning operational insight and threat realities into clear direction for customers, teams and management.
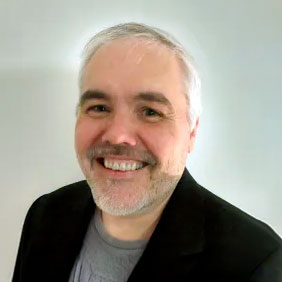
David Kasabji
Head of Threat Intelligence, Conscia Cybersecurity
Jesper Kastoft Bertelsen
Director of Cyber Defense Services, Conscia Cybersecurity
Andrew Michal
Senior Cybersecurity Engineer, Conscia Cybersecurity
Date & time
October 29, 2026 - 10:00 - 11:00 (CET)
Where
Online
Language
English
Target audience
This webinar is designed for:
-
- CISOs and security leaders
-
- CIOs and IT decision-makers
-
- Risk and compliance professionals
-
- Executive leadership teams
-
- Board members responsible for cyber resilience and governance
Whether you are setting cyber strategy, managing security operations or overseeing organisational risk, this session will help you connect operational evidence to the decisions that shape cyber resilience, investment priorities and risk governance.
Important Update for All Using Certificates for Single Sign-On
Do you use Kerberos SSO with certificate-based authentication (CBA), e.g., for validating intranet and file/print servers? If so, read on! Since May 2022, Microsoft has been working on initiatives to ...
Related