
Conscia MDR
Managed Detection and Response (MDR) services that keep your organisation secure, resilient, and ready to respond.
High visibility. Fast disruption. Business continuity.
Modern Managed Detection and Response (MDR) services promise to make all incidents negligibly small through fast threat detection and disruption.
Conscia MDR goes the extra mile, by giving you the broadest threat coverage (on-prem, cloud, OT, IoT, or IoMT), lowest ops workload, integrated access to Conscia Digital Forensics and Incident Response team, and continuous expert recommendations to enhance your security posture. By disrupting criminal activities in seconds or minutes, we ensure the highest level of your business continuity in face of modern risks
Managed Detection and Response (MDR) that fits your risk profile like a glove.
If your environment is subject to specific risks, or has specific challenges, Conscia MDR has a number of optional modules to address those risks:
- Conscia Instant Response, which isolates selected assets at the first sign of compromise, and releases them quickly for false positives
- supply chain monitoring, using external and internal threat intelligence, fully integrated into MDR response workflows
- managed exposure (vulnerability) assessment, including EASM, with advanced analytics and recommendations
- identity intelligence and brand protection (via clear and dark web monitoring)
- insider risk management and data leakage detection with Microsoft Purview
- full DFIR services with custom SLAs
- strategic threat intelligence consulting
- managed log management
Built for the age of AI threats and supply chain risks
Attackers now move faster than any human analyst can triage. AI-assisted attacks can spread through a network within minutes. That’s why Conscia MDR offers Instant Response: on the assets you choose, we contain first and investigate second. At the first suspicious signal, the device is isolated and the identity locked. If the alert turns out to be harmless, the asset is released automatically, typically within 10–15 minutes.
Your partners can also be a way into your environment. Supply Chain Monitoring checks your suppliers’ security posture every day and watches the dark web for their leaked credentials. Each partner’s risk is weighted by how much access they have to your systems. If a supplier’s stolen credentials can reach your services, you get a real-time alert and our response starts straight away. Both capabilities are available as optional modules, so you can build the protection your organisation needs.
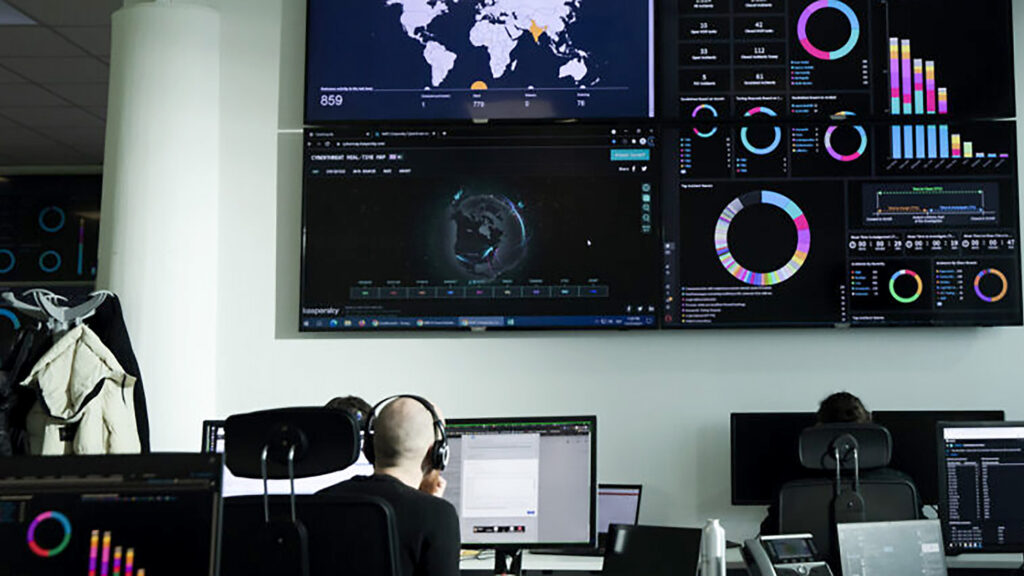
Get to know our SOC and MDR
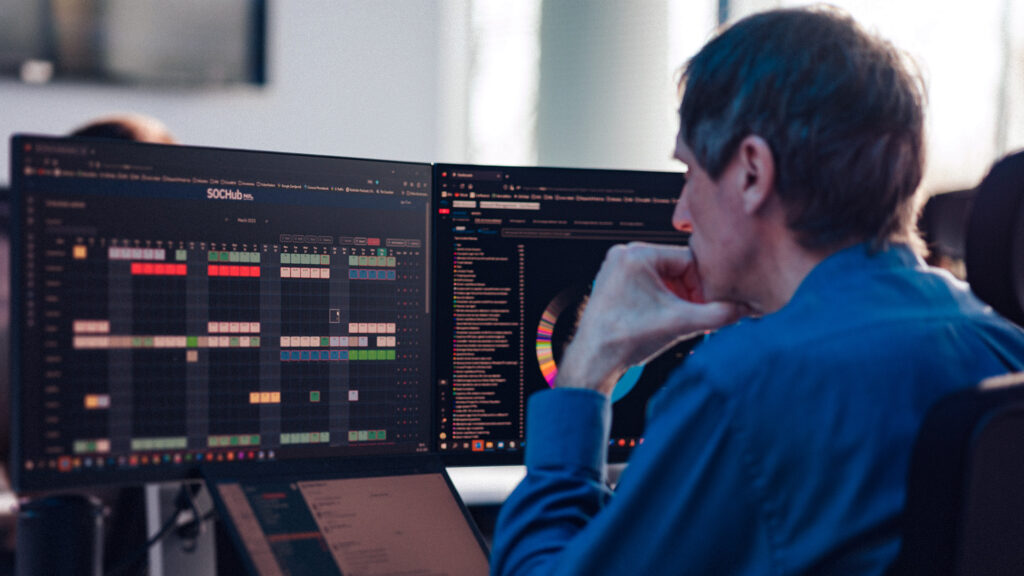
What is MDR? Conscia’s Approach to Managed Detection & Response
Traditional security tools can only make the “doors” smaller. Attackers still get in. That’s why Managed Detection and Response (MDR) has become one of the most effective ways to reduce cyber risk to a manageable level.
In this video, Jan Bervar, Group Security Architect at Conscia, and Matic Jerman, MDR Operations Manager at Conscia, explain:
- Why MDR is a business enabler, not just a cost centre
- The two pillars of modern MDR: threat intelligence and operations
- How Conscia’s focus on rapid response and automation reduces customer workload
- What a day in an MDR “emergency department” actually looks like
- How the rise in supply chain and phishing attacks is changing detection strategies
At Conscia, security isn’t just about people, processes, and technology. It’s about the passion that goes beyond the process. That’s Secure Progress.
Levels of Conscia MDR Service
Standard
- 24×7 MDR services providing detection and response in minutes
- Fast attack disruption through rich set of response actions
- Microsoft Defender XDR platform for broad threat coverage
- Conscia MDR service portal access
Premium
- 24×7 MDR services providing detection and response in minutes
- Fast attack disruption through rich set of response actions
- Dedicated consultants provide monthly expert reporting and defense improvement recommendations
- Choice of several XDR platforms for flexible and broad threat coverage
- Conscia MDR service portal and mobile application access
- Premium features, such as custom SaaS and PaaS support, custom escalation processes. and vulnerability management analytics dashboard
- Easy access to optional managed services, such as exposure management, managed EASM, managed deception, threat intel briefings, brand protection, and dark web monitoring
Enterprise
- 24×7 MDR services providing detection and response in minutes
- Fast attack disruption through rich set of response actions
- Dedicated consultants provide monthly expert reporting and defense improvement recommendations
- Incident response costs included
- Choice of several XDR and managed SIEM platforms
- Conscia MDR service portal and mobile application access
- Premium features as in the Premium package
- Enterprise features, such as dynamic enterprise asset classification, business unit analytics, and ITSM integration
- Easy access to optional managed services, such as exposure management, managed EASM, managed deception, threat intel briefings, brand protection, and dark web monitoring
Success stories
From our knowledge hub
Security is just the start
Networking
We design and manage robust, reliable networks that scale with you, from first rollout to everyday performance.
Hybrid cloud
We combine on-premises and cloud infrastructure into a secure, scalable environment – tailored to your needs today and ready for whatever comes next.
Observability
Complex IT environments multiply blind spots and widen the margin for error. Sometimes, all you need is a bird’s-eye view.